- SMB1 is an obsolete and vulnerable protocol whose deactivation significantly improves system security against threats such as WannaCry.
- SMB2 and SMB3 should be kept active, as they provide key improvements in performance, encryption, and high availability compared to SMB1.
- SMB and other legacy service management can be done from PowerShellRegistry, graphical interface or via Group Policy in corporate networks.
- Reviewing optional services and features such as Fax, XPS, or legacy network components reduces the attack surface and simplifies operations. Windows.

Many Windows systems still carry over legacy features that almost no one uses but that continue to consume resources and can even create security vulnerabilities. We're talking about services like Fax, XPS, and the outdated SMB1 protocol , as well as a number of optional features that Microsoft maintains for compatibility but which are completely unnecessary on a modern home or office PC.
With a little tweaking of the configuration, it's possible to disable these legacy services , reduce the attack surface against ransomware -type threats , and lighten the system somewhat. However, before touching anything, it's essential to understand the purpose of each component, its dependencies, and how to manage it correctly , whether through the graphical interface, PowerShell, the Registry, or even Group Policy in enterprise environments.
What is SMB (SMB1, SMB2 and SMB3) and why does it matter so much?
The Server Message Block (SMB) protocol is the foundation for sharing files, printers, and other resources on Windows networks. It allows a computer to act as a file server, enabling other computers to access that data as if it were local, and also manages remote operations such as reading, writing, and locking files.
Over the years, Windows has incorporated successive versions of the protocol : SMB1, SMB2, and SMB3. Each upgrade has brought improvements in performance, security, and scalability, so that today the recommended version is SMB3 , while SMB1 is considered completely obsolete and dangerous.
SMB1 was used exclusively in systems like Windows XP and Windows Server 2003 , which are no longer supported or patched. Many older devices (old NAS devices, network printers, poorly configured Linux systems ) also still rely on this version for compatibility, sometimes requiring it to be kept active on modern servers or clients.
The problem is that SMB1 has critical vulnerabilities that have been exploited by well-known malware , such as the WannaCrypt/WannaCry ransomware . This family took advantage of a flaw in the SMBv1 implementation to spread from one computer to another within the network, without requiring user interaction.
For this reason, Microsoft has been removing SMB1 from modern installations: Windows 11 and Windows Server 2019 and later versions do not include it by default , and in Windows 10 it is only retained in some Home and Pro editions if certain applications require it. Even so, in many environments it remains installed or even active, and it is highly recommended to remove or disable it whenever possible.
What do we lose (and what do we gain) by disabling SMB1, SMB2, or SMB3?

The general recommendation is clear: disable SMB1 on all devices that don't strictly require it, and leave the modern versions SMB2 and SMB3 active. Even so, it may sometimes be useful to temporarily disable SMB2/3 to diagnose a compatibility, performance, or unusual network behavior issue.
Disabling SMBv3 results in the loss of several important advanced features in high-availability environments , as many are specific to modern versions of Windows Server and file clusters. For example, the following are disabled:
- Transparent failover: allows clients to reconnect to another node in a cluster without the user noticing the failure.
- Horizontal scalability: simultaneous access to the same shared data from multiple nodes in the cluster.
- Multichannel SMB: simultaneous use of multiple network paths to aggregate bandwidth and gain fault tolerance.
- SMB Direct (RDMA): support for very high-speed RDMA networks, with low latency and low CPU usage.
- End-to-end encryption: protection against eavesdropping and attacks on untrusted networks.
- Directory leasing and other optimizations to improve latency and performance in remote branches.
If we disable SMB2 instead of SMB3 , the impact is also significant. SMB2 introduced key improvements over SMB1:
- Grouping of petitions (batching) to send multiple requests in a single network packet.
- Larger readings and writings that take advantage of Gigabit and higher links.
- Storage cached properties of files and folders to reduce access to the server.
- Durable identifiers that allow reconnection without losing sessions after brief interruptions.
- Reinforced message signature with HMAC SHA-256 instead of MD5.
- Greater scalability in number of users, shared resources and files opened per server.
- Support of symbolic links and a concession model that improves performance in high-latency networks.
- Large MTU to take full advantage of 10 GbE links.
- optimizations of Energy Efficiency to suspend clients with open files.
In other words, disabling SMB2 or SMB3 only makes sense as a temporary diagnostic measure . What should be done permanently is to remove SMB1 , always checking beforehand if there are any older devices that might lose access.
How to check, enable, or disable SMB1 from PowerShell
In modern systems such as Windows 10, Windows 11 or Windows Server 2016/2019 , the cleanest way to manage SMB1 is by using PowerShell with administrator privileges, relying on optional system features.
To view the current status of the SMB1 client/server on Windows, you can use the Get-WindowsOptionalFeature cmdlet , pointing to the specific feature:
Get-WindowsOptionalFeature -Online -FeatureName SMB1ProtocolIf the goal is to disable SMB1 (the recommended case), simply run:
Disable-WindowsOptionalFeature -Online -FeatureName SMB1ProtocolAnd if, for compatibility reasons, there is no other option but to reactivate it , it can be done with:
Enable-WindowsOptionalFeature -Online -FeatureName SMB1ProtocolIn server editions such as Windows Server 2012 R2 and 2016 , SMB1 is packaged as a role feature. In those cases, it can be removed directly from PowerShell with:
Remove-WindowsFeature FS-SMB1It's important to remember that many changes to optional features and roles require a system restart to take full effect, so it's advisable to plan your maintenance window, especially on production servers.
Managing SMB1, SMB2, and SMB3 from the Registry (server and client)
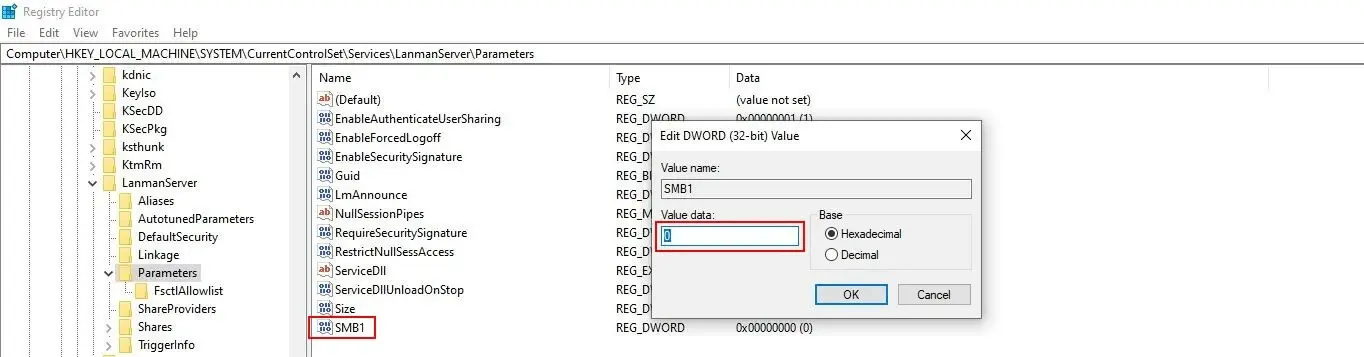
In older versions of Windows or when very fine control is needed, it's possible to enable or disable SMB from the Registry . This technique applies to both Windows Server (SMB server role) and workstations acting as clients.
For an SMB server , the main configuration key is:
HKEY_LOCAL_MACHINE \ SYSTEM \ CurrentControlSet \ Services \ LanmanServer \ Parameters
The following values can be created in that path (if they do not already exist) :
- SMB1 (REG_DWORD):
Value 0 = protocol disabled
Value 1 = protocol enabled (default) - SMB2 (REG_DWORD):
Value 0 = disables SMB2 and SMB3, since they share an internal stack
Value 1 = enables SMB2/3 (default)
These values can be manipulated from PowerShell using cmdlets like: Set-ItemProperty
Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\LanmanServer\Parameters" SMB1 -Type DWORD -Value 0 -Force

Set-ItemProperty -Path "HKLM:\SYSTEM\CurrentControlSet\Services\LanmanServer\Parameters" SMB2 -Type DWORD -Value 0 -Force
In the case of the SMB client on Windows , things change because it depends primarily on the LanmanWorkstation service and the mrxsmb10 (SMB1) and mrxsmb20 (SMB2/3) drivers. The command-line tool sc.exe is typically used here to adjust dependencies and startup mode.
To manage SMB1 on the client, commands such as the following can be used :
sc.exe qc lanmanworkstationThis verifies the current service configuration . To disable the SMB1 client portion, the dependency is updated and the corresponding driver is deactivated.
sc.exe config lanmanworkstation depend= bowser/mrxsmb20/nsi
sc.exe config mrxsmb10 start= disabled
If it becomes necessary to reactivate the SMB1 client later , it would be enough to restore the dependency and the automatic startup of the controller:
sc.exe config lanmanworkstation depend= bowser/mrxsmb10/mrxsmb20/nsi
sc.exe config mrxsmb10 start= auto
A similar pattern applies when the goal is to keep SMB1 operational but disable SMB2/3 on the client, modifying in this case the behavior of mrxsmb20.
Disable SMB1 using Group Policy (GPO)
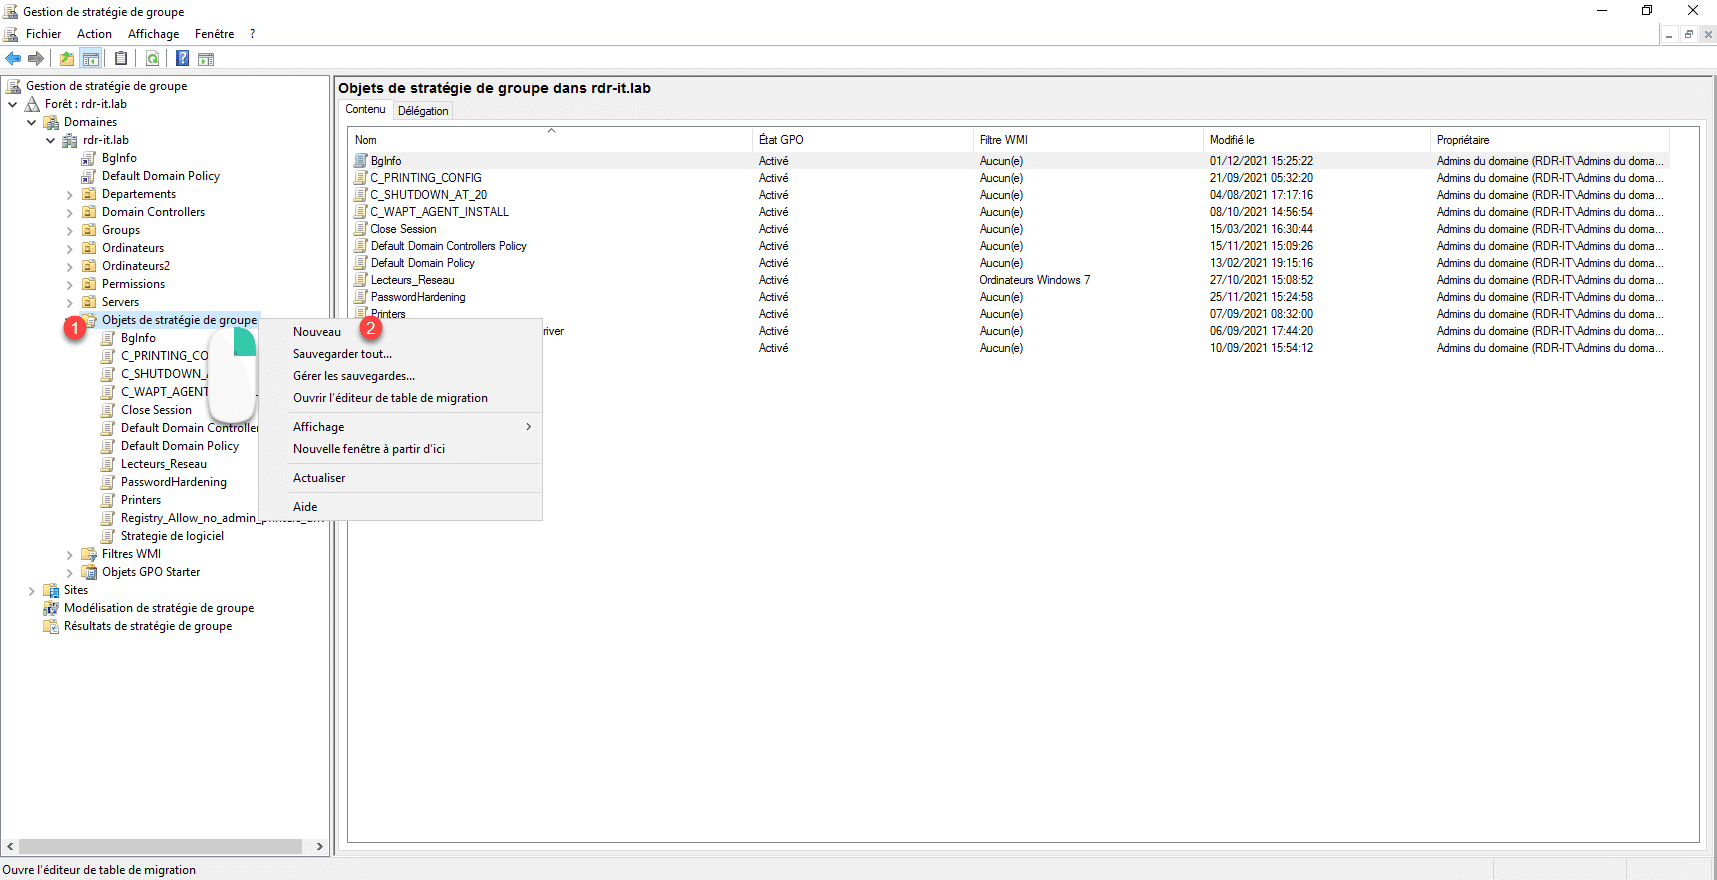
In corporate networks with many computers, going machine by machine is impractical. The most efficient approach is to leverage Group Policy (GPO) to deploy registry changes that centrally disable SMB1 on member workstations and servers.
The trick is to play two main keys :
- HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\services\mrxsmb10
Value: Start (REG_DWORD) = 4 → service disabled. - HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\LanmanWorkstation
Value: DependOnService (REG_MULTI_SZ) = Bowser, MRxSmb20, NSI (without MRxSMB10).
In the policy management console, a new Registry Item is created within the Computer Configuration > Preferences > Windows Settings > Registry branch. The first is configured as Action = Update, pointing to the Start value of mrxsmb10 and setting data to 4. The second is created as Action = Replace, defining the multi-SZ DependOnService with the strings Bowser, MRxSmb20, and NSI.
Applying the GPO and restarting the target machines will prevent the client from loading or relying on MRxSMB10 , effectively disabling SMB1. To force a refresh during testing, the following command can be run on the clients:
gpupdate /forceIt is advisable to then validate that SMB2 and SMB3 continue to function correctly in the rest of the systems and that connectivity with critical shared resources has not been broken.
Audit which teams are still using SMB1
Before taking drastic measures, it's very useful to audit who is trying to connect via SMB1 . This helps avoid problems with old printers, outdated NAS devices, misconfigured Linux systems, or even Windows machines forgotten in a corner.
In modern versions of Windows Server, it's possible to enable specific auditing using the Set-SmbServerConfiguration and Get-SmbServerConfiguration cmdlets . To start logging SMB1 accesses, run:
Set-SmbServerConfiguration -AuditSmb1Access $trueIf at any time you want to disable auditing , simply change the value to false:
Set-SmbServerConfiguration -AuditSmb1Access $falseTo check the current status of this configuration, you can consult:
Get-SmbServerConfiguration | Select AuditSmb1AccessOnce auditing is enabled, each connection attempt using SMB1 generates an event in the Microsoft-Windows-SMBServer\Audit log with event ID 3000. Reviewing these events provides a fairly reliable list of clients that still depend on SMB1 , allowing you to plan their migration or replacement before permanently disabling the protocol.
Enable or disable SMB 1.0 from the graphical interface
In some versions of Windows, it's possible to configure SMB 1.0 directly from the GUI without touching PowerShell or the Registry. This mainly applies to:
- Windows 8.1 and Windows 10 (client editions).
- Windows Server 2012 R2 and Windows Server 2016.
On client computers, the typical path is to go to Control Panel > Programs and Features (or run appwiz.cpl ), and then select "Turn Windows features on or off." Within the list, you'll find the entry "SMB 1.0/CIFS file sharing support ," which can be unchecked to disable SMB1.
In server editions such as Windows Server 2012 R2 or 2016, the process involves using Server Manager . From the "Remove roles and features" option, access the Features section and uncheck "SMB 1.0/CIFS file sharing protocol support." Once the wizard has been applied, a server restart will be required to complete the uninstallation.
Deactivate other legacy services: Fax, XPS, and others
In addition to SMB1, Windows comes loaded with optional features that most users don't need in practice. While you won't always see huge performance improvements, it is possible to reduce complexity, memory consumption, and, above all, the attack surface by having fewer exposed components.
Some of the most common features that can be reviewed in “Turn Windows features on or off” are:
- XPS Services and XPS ViewerThe XPS format was proposed as an alternative to PDFBut it never really caught on. Windows 10 and 11 already integrate PDF printing and reading, so maintaining XPS is usually unnecessary.
- Windows Fax and Scan: useful only if a physical fax machine or integrated scanner Managed through Windows tools. If you use the manufacturer's own scanner or don't use fax, you can safely disable it.
- Windows Media Player and player network sharingThe popular WMPNetworkSvc service allows you to share media libraries over a network. If alternative players are used, or if no media is shared, the system will function correctly. streaming internal, is another clear candidate to be disabled.
- Legacy components (DirectPlay): only necessary for very old games that depend on this DirectX network API. If you don't play classic titles online, you can usually disable it.
It's also advisable to review services that load in the background and are of little use on a home computer. Typical examples in Windows 7/10 include Fax , Bluetooth Support Service (if you don't use Bluetooth), Net Logon on non-domain computers, and SNMP , which is intended for monitoring corporate networks.
Other Windows services that can usually be disabled
In scenarios where the goal is to maximize performance (for example, on a gaming PC), it's common to review the list of Windows services and disable anything that's never used . However, it's advisable to do this carefully, ideally after creating a system restore point so you can revert to the previous state if something goes wrong.
Among the services that are often considered dispensable in a domestic environment (provided their specific functions are not needed) are:
- Windows Search (WSearch)It maintains an index of files, emails, and other content to speed up searches. If you rarely use the built-in search engine, you might consider disabling it.
- Windows Media Player Network Sharing Service (WMPNetworkSvc): responsible for sharing multimedia libraries on the local network.
- SNMP Capture (SNMPTRAP) y Simple Network Management Protocol (SNMP): geared towards advanced network monitoring. Unnecessary in most homes.
- Services related to smart cards (SCPolicySvc, SCardSvr, Certificate Propagation): provide support for environments that use smartcard authentication.
- Remote Registry (RemoteRegistry): allows modifying the Registry from other computers, which is risky in uncontrolled environments.
- Offline Files (CscService): useful only if you use the feature of offline files in corporate networks.
- Network Access Protection Agent (napagent): old part of Microsoft's NAP infrastructure.
- Net Logon (Netlogon): essential in domain-joined systems, but completely unnecessary in home PCs.
- iSCSI Initiator Service (MSiSCSI): only if you connect to remote iSCSI devices.
- Distributed Link Tracking Client (TrkWks): maintains links NTFS between equipment and volumes.
- BranchCache (PeerDistSvc): designed to optimize WAN traffic in company branches.
- Bluetooth Compatibility Service (bthserv): only necessary if you use Bluetooth devices.
- Adaptive brightness (SensrSvc): automatically adjusts brightness based on ambient light sensors.
- WinHTTP Auto Proxy (WinHttpAutoProxySvc): detects automatic proxies; in simple networks it is usually unnecessary.
- Windows Remote Management (WinRM): used for remote management via PowerShell and other tools.
- Windows Error Reporting Service (WerSvc): sends crash reports to Microsoft.
- Windows Color System (WcsPlugInService): focused on advanced color profile management.
- Application-Level Gateway (ALG) Service: related to Internet Connection Sharing (ICS).
- BitLocker Drive Encryption Service (BDESVC) y Encrypting File System (EFS): redundant if these encryption methods are not used.
- Access to human interface device (hidserv): provides extra functions to special keyboards and controllers.
- Remote Desktop Services (TermService, UmRdpService, SessionEnv) and Remote Desktop Configuration: only required if you connect via Remote Desktop or host other machines.
- Tablet PC Input Service (TabletInputService): stylus support and touch writing.
- Windows Biometric Service (WbioSrvc): for fingerprint readers, facial recognition, etc.
The list is long, and not all services will be available in every version of Windows. The key is to understand that any changes should be made knowing which services you shouldn't disable , especially on computers used for work or that are part of a larger network.
Advanced optional features: when to have them enabled
The Windows optional features panel also houses components designed for professional or development environments , which most home users will never touch. Disabling them doesn't always provide significant benefits, but it does help to "clean up" the system of superfluous items.
Some typical examples are:
- .NET Framework 3.5 (includes 2.0 and 3.0) y Advanced services of .NET Framework 4.xThese are necessary if you run applications that depend on these versions. If you disable them and later install a program that requires .NET, Windows usually offers to install it on demand.
- Active Directory Lightweight Directory Services y Windows Identity Foundation: technologies focused on authentication and directories, especially in business environments.
- Internet Information Services (IIS) and hostable web core: they only make sense if you're going to set up a web or FTP server local for development or testing.
- Hyper-VMicrosoft's virtualization solution. It's very powerful, but not essential if you already use alternatives like VirtualBox o VMware for specific tests.
- Telnet Client, TFTP Client, Connection Manager Administration Kit o Microsoft Message Queue: inherited from other eras or intended for very specific uses of remote administration and development.
- Printing and document services Advanced features (LPR, LPD, scan management, internet print client): these are usually unnecessary on computers that only print to one printer USB or conventional home WiFi.
- Simple TCPIP Services, Listen to RIP and similar utilities: they belong to complex network scenarios and are usually disabled in most installations.
The key is to review the list carefully, always considering whether you truly need each item. If in doubt, it's best to leave it enabled or do some further research before making any changes, especially when dealing with production equipment or everyday work tools.
Leaving SMB1 behind, disabling legacy services like Fax or XPS, and adjusting optional features to what you actually use is a simple way to have a more secure, lightweight Windows that's better suited to your needs , avoiding ransomware scares and reducing features that are only there "just in case" but, on most current PCs, no longer provide any useful benefit.


Passionate writer about the world of bytes and technology in general. I love sharing my knowledge through writing, and that's what I'll do on this blog, show you all the most interesting things about gadgets, software, hardware, tech trends, and more. My goal is to help you navigate the digital world in a simple and entertaining way.
Table of Contents
- 1 What is SMB (SMB1, SMB2 and SMB3) and why does it matter so much?
- 2 What do we lose (and what do we gain) by disabling SMB1, SMB2, or SMB3?
- 3 How to check, enable, or disable SMB1 from PowerShell
- 4 Managing SMB1, SMB2, and SMB3 from the Registry (server and client)
- 5 Disable SMB1 using Group Policy (GPO)
- 6 Audit which teams are still using SMB1
- 7 Enable or disable SMB 1.0 from the graphical interface
- 8 Deactivate other legacy services: Fax, XPS, and others
- 9 Other Windows services that can usually be disabled
- 10 Advanced optional features: when to have them enabled