- Baiting is a social engineering technique that uses physical or digital devices to deceive victims and steal information.
- Attackers can use USB infected, fake ads or downloads free to distribute malware.
- The best way to avoid being a victim of baiting is to avoid connecting unknown devices and keep your security systems up to date.
- Baiting attacks can affect both individuals and businesses, compromising confidential information and causing financial losses.

Baiting is one of the most common social engineering attacks used by cybercriminals to trick people into gaining access to their devices or personal data. It's a tactic where the attacker offers something enticing, such as a USB drive found on the street or a free download online, with the goal of getting the victim to use it and unknowingly infect their computer with malware.
This type of attack can cause significant losses for both individual users and businesses, as the installed malware allows the theft of sensitive information, remote system access, or the spread of viruses on corporate networks. Below, we'll explain in detail how baiting works and what measures you can take to protect yourself.
What is baiting and how does it work?
Baiting, also known as a lure attack, is an attack technique that exploits user curiosity and trust. Unlike phishing, which uses fraudulent emails or messages, baiting relies on a seemingly harmless physical or digital asset.
Attackers use various strategies to carry out this deception:
- Infected USB devices: Cybercriminals leave USB drives in strategic locations, such as offices or parking lots, with eye-catching labels like "Confidential Information" or "Payment List." When the victim plugs the USB into their computer, the malware is automatically installed.
- Free downloads: Fake websites are used to offer free software, music, or movies in exchange for the user downloading a file that actually contains malware.
- Deceptive emails and ads: Emails are sent containing links to fraudulent sites or ads are placed on social media promising unrealistic prizes or discounts.
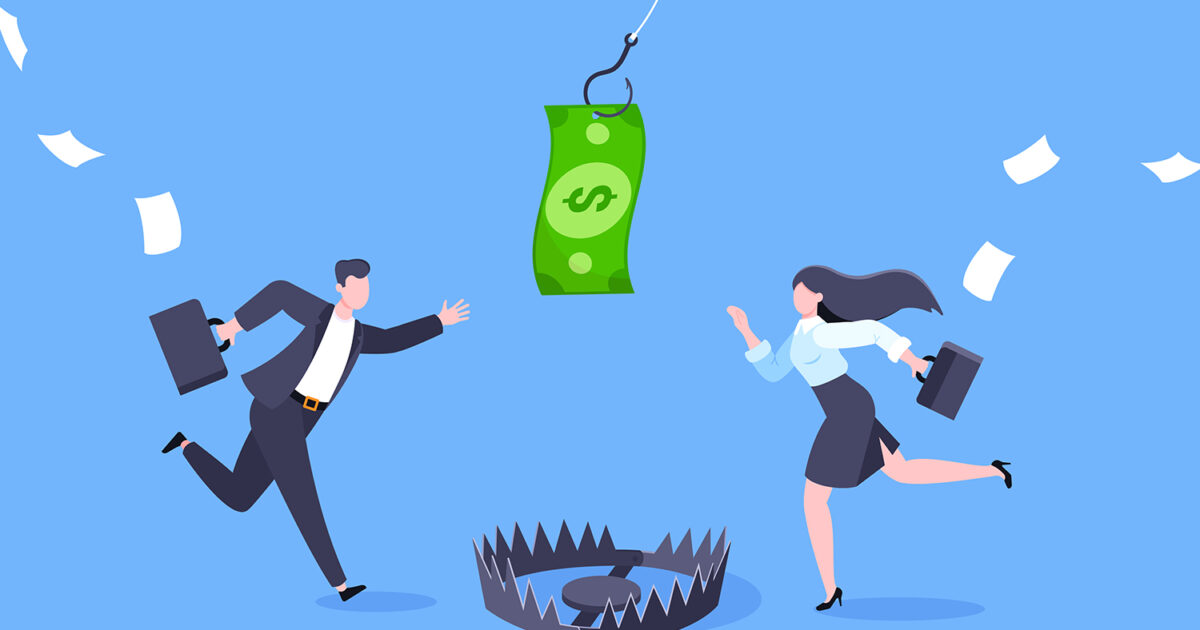
Once the victim falls for the trap and executes the file or connects the compromised device, the malware can:
- Robar access credentials and personal data.
- Install Trojans that allow remote control of the device.
- Encrypt important files and require a ransom payment (ransomware).
- Spy on user activity and record keystrokes (keyloggers).
Real-life cases and examples of baiting attacks
Baiting is not just a theory, but a technique that has been successfully used on numerous occasions. One of the most well-known cases was an experiment conducted at an American university in which 297 USB drives were distributed on campus. Forty-five percent of them were connected to computers without any prior verification, demonstrating the effectiveness of the attack.
Another notable case was the FBI's 2021 warning about a baiting campaign targeting businesses and government agencies. Attackers sent infected USB drives as supposed promotional gifts, successfully compromising multiple corporate networks.

How to protect yourself from baiting
To avoid becoming a victim of these types of attacks, it is essential to adopt good security practices . Here are some of the most effective:
- Do not connect unknown USB devices: Whenever you find a USB or any other storage device storage If it's unowned, avoid connecting it to your computer. If you work for a company, inform the IT department.
- Always keep your antivirus and security software up to date: Up-to-date protection software can detect and block malware from running.
- Disable autoplay of external devices: Configure your computer to not automatically run content from an inserted USB.
- Be wary of downloads and offers that are too good to be true: Many fraudulent websites offer supposed promotions or free software with the aim of distributing malware.
- Training and awareness on ciberseguridad: In the corporate environment, it is essential to educate employees about the risks of baiting and how to identify potential threats.
If you suspect your computer has been infected by a baiting attack, follow these steps:
- Disconnect the infected device: If you plugged in a suspicious USB, remove it immediately.
- Isolate the equipment from the network: Disconnecting it from the Internet or the corporate network can prevent malware from spreading.
- Perform a scan with antivirus software: Run a full system scan to identify and remove any threats.
- Change your account passwords: If malware has stolen credentials, it's crucial to update all your passwords immediately.
- Consult a cybersecurity expert: In the event of a serious infection, a computer security specialist can help you mitigate the damage.

Baiting is a highly effective attack technique due to human curiosity. By being well-informed and adopting proper security habits , you can significantly reduce the risk of falling into these traps. Prevention and cybersecurity education are key to keeping your devices and personal data safe.


Passionate writer about the world of bytes and technology in general. I love sharing my knowledge through writing, and that's what I'll do on this blog, show you all the most interesting things about gadgets, software, hardware, tech trends, and more. My goal is to help you navigate the digital world in a simple and entertaining way.