- Malvertising uses seemingly legitimate advertisements to distribute malwarescams and malicious redirects without requiring the user to click.
- This technique can exploit vulnerabilities in browsers, plugins, and systems to launch downloads to carry and load ransomware, spyware, adware or cryptominers.
- It is a threat that affects Windows, macOS, mobile devices and business environments, even reaching major media outlets and online services.
- The combination of up-to-date security software, ad blockers, current systems, and good browsing habits significantly reduces the risk.
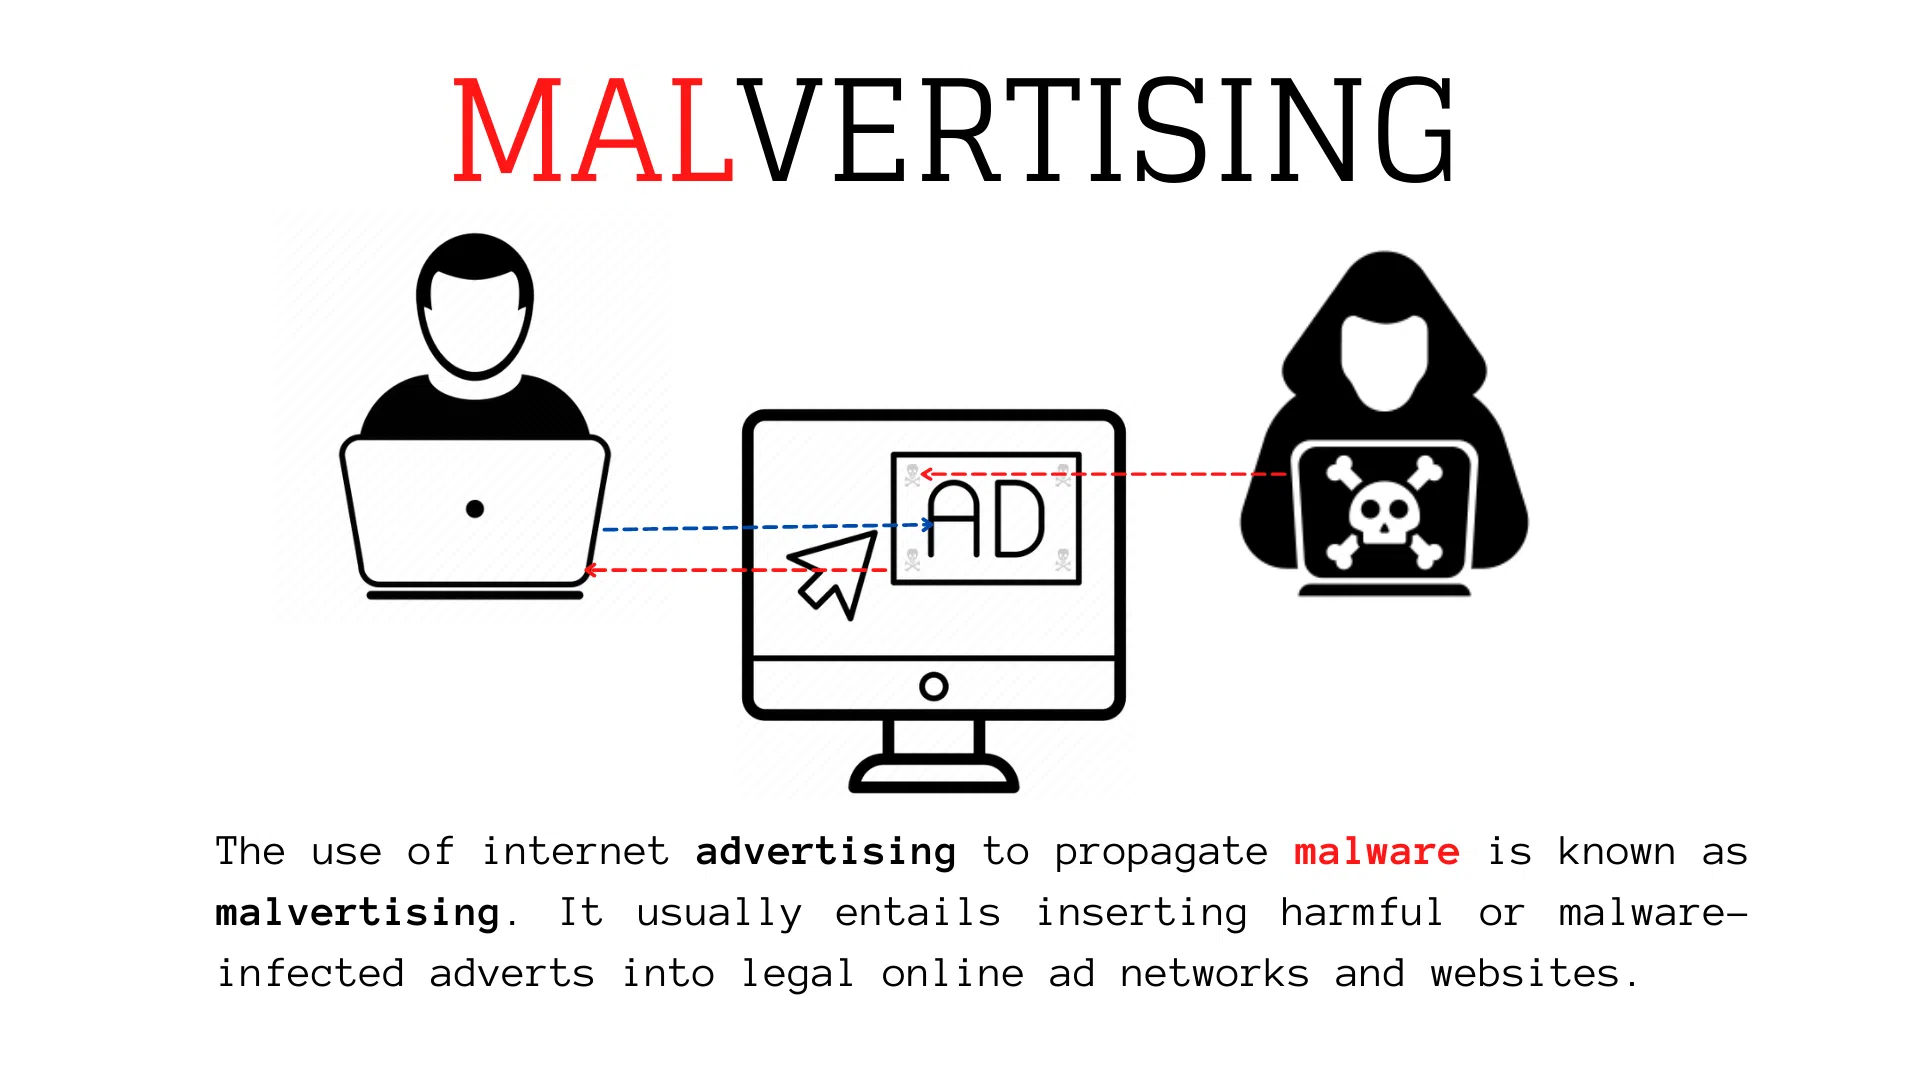
The next time you see an eye-catching ad while browsing peacefully, keep in mind that it's not always just harmless advertising . Behind an attractive banner, an annoying pop-up , or an offer that seems too good to be true, a malvertising attack could be lurking, ready to infect your device even if you do nothing more than load the page.
This technique has become a favorite method of cybercriminals because it exploits legitimate advertising and trust in well-known websites to sneak in all kinds of malware: ransomware, spyware, Trojans, adware, and much more. Let's take a closer look at exactly what malvertising is, how it works, what types exist, what damage it can cause, and, above all, how you can minimize the likelihood of falling into this trap.
What is malvertising or malicious advertising?
The term malvertising comes from combining the English words "malicious" and "advertising ." It refers to the use of online ads as a vehicle for spreading malware, scams, and other dangerous content. The key is that the attack infiltrates legitimate advertising spaces , usually managed by large ad networks, and ends up appearing on pages that the user perceives as safe and trustworthy.
Instead of directly attacking the website or company displaying the ads, criminals infect ad creatives or advertising supply chains . This way, the ads appear normal, are distributed through legitimate platforms, and ultimately reach thousands or millions of users without raising suspicion.
Malvertising can work in two main ways: through clicks on the ad , which lead the user to fraudulent sites or malicious downloads, or through drive-by downloads , where simply viewing the page containing the ad is enough for the attack to be executed by exploiting flaws in the browser, in plugins such as Flash or Java, or in the system itself.
The most worrying thing is that we are talking about a technique that barely requires interaction: in many cases, the user doesn't even have to click on the ad to end up compromised, which makes it a stealthy threat and difficult to detect at first glance.
How a malvertising attack works
To understand why it's so effective, it's helpful to see how a typical malvertising attack is orchestrated, from the moment the attacker prepares the campaign until the user is infected without realizing it. It all relies on the standard workings of online advertising, which are based on ad networks, automated bidding, and mass distribution.
First, attackers create or manipulate ads (banners, text ads, videos, pop-ups, etc.) and inject malicious code, scripts, or hidden redirects into them . These ads typically meet the visual and technical standards of advertising platforms, so they pass basic filters relatively easily.
Next, they send these creative assets to legitimate advertising networks or intermediaries (ad exchanges, programmatic buying platforms, etc.), which distribute them to thousands of websites that monetize their content with ads . Often, neither the advertising network nor the publisher has full visibility into all the code behind each banner, so the attack goes undetected.
When a user visits a page with this type of ad, the browser sends a request to the ad network and loads the malicious creative along with other normal ads . From here, two things can happen: the user might click on the ad and be redirected to a fraudulent website, or the mere act of displaying the ad might trigger, in the background, an exploit that attempts to take advantage of vulnerabilities in the browser, plugins, or the system.
In the case of walkthrough downloads, an invisible iframe or page elements that the user neither sees nor interacts with are typically used. These resources load an exploit kit that analyzes the system: browser version, installed plugins, operating system, location, etc. Based on this information, the command and control server decides which type of malware is most profitable to install on that specific machine.
Types of campaigns and malvertising techniques
Over the years, malvertising has evolved from exploiting very specific vulnerabilities (as happened with Adobe Flash in the first documented cases in 2007-2008) to deploying a fairly broad catalog of tactics and tricks to bypass controls and maximize the effectiveness of infections. These are some of the most common methods.
Steganography in advertisements
Steganography involves hiding information within other information in a way that makes it completely undetectable. In the context of malvertising, attackers conceal malicious code within seemingly normal images: a banner, a product photo, or any graphic that is part of an advertisement.
Malware can hide in a small area of pixels or in the image metadata; the advertising network and the user see a standard file with nothing unusual, but when the ad loads, the embedded code is extracted and executed by associated scripts. This technique greatly complicates detection, even for advanced security solutions.
Polyglot images
So-called polyglot images take this a step further: they are files capable of behaving simultaneously as a valid image and as another type of executable file or script . In practice, this allows both the malicious payload and the code needed to launch it to travel within a single image.
Because they don't rely on visible external scripts, ads using polyglot images are more autonomous and harder to filter . The file can be interpreted simultaneously by the browser as a graphic resource and by the JavaScript engine as code to be executed, without the user noticing anything unusual in the interface.
Scareware and alarmist pop-ups
Another classic form of malvertising is scareware: ads or pop-ups designed to frighten you with alarmist messages like “Your PC is seriously infected,” “Your system is damaged,” or “45 viruses have been detected.” The goal is to create a sense of urgency so you click the “fix now” or “scan for free” button.
By accessing this supposed “antivirus” or “cleaner,” you are actually downloading malware disguised as a security or optimization tool . In other versions of the scam, you are sent to websites that mimic the operating system or browser, displaying fake security scans to trick you into paying for a nonexistent cleanup.
Tech support scams
Closely related to scareware are tech support scams. These ads redirect you to pages that impersonate Microsoft, Apple, or other major brands , displaying error messages and "technical support" phone numbers. The browser may even lock your screen with persistent dialog boxes, preventing you from closing it normally.
If you call the number, you'll be answered by fake agents who ask for remote access to your computer, personal information, or payment for a "repair" service that not only doesn't fix anything but often leaves even more malware installed. This type of fraud has been very prevalent among Windows and Mac users and is largely fueled by malvertising campaigns.
Get rich quick scams and fake surveys
Another common lure in malvertising campaigns is the promise of easy money, incredible sweepstakes, or surveys with exorbitant prizes . You've probably seen banners offering unrealistic monthly income, prizes like the latest smartphones, or gift cards simply for filling out some information.
Behind these campaigns can be anything from aggressive data collection strategies to the installation of adware, spyware, or even ransomware . The pattern is always the same: content that seems too good to be true, but is actually designed to lead you to infected websites or trick you into entering personal information without any guarantees.
Fake software updates
Fake updates are one of the most effective lures, especially on streaming or download sites. The ad claims you need to update Flash Player, your browser, a video codec, or some other program to continue watching what you want. In some cases, an installer is even downloaded automatically when you visit the page.
If a user installs this supposed update, they end up introducing spyware, adware, Trojans, or other malware into their system , often bundled with a seemingly functional program to reduce suspicion. That's why it's so important to download software and updates only from official websites and not from banners or pop-up windows.
Malvertising versus adware: what are the differences?
Although the two concepts are often confused, it's important to distinguish between malvertising and adware, because they are not the same and they don't operate in the same way . Both combine advertising and potentially harmful intentions, but their starting point and methods differ.
In malvertising, the problem lies in advertising networks and campaigns . The ad arrives already infected from the advertising infrastructure and uses that channel to sneak malware onto the user's device. The infection occurs through the ad itself or the chain of redirects associated with it.
In the case of adware, an unwanted program is first installed on your computer (often included in free software installers or bundled with other apps ), and from then on, that program is the one that displays intrusive ads . In other words, the infection is already on the device and not on the ad network.
While malvertising can be used to distribute anything (ransomware, spyware, banking trojans, cryptocurrency miners , etc.), adware usually focuses on generating revenue through the mass display of advertising , although it sometimes also serves as a gateway for more serious threats.
History and evolution of malvertising
The first documented malvertising attacks date back to late 2007 and early 2008 , when an Adobe Flash vulnerability was exploited to infect popular sites such as MySpace and Rhapsody. Since then, the complexity and scope of these campaigns have steadily increased.
In 2009, even a prestigious publication like The New York Times was affected by an advertisement that enrolled companies in a massive botnet . Readers were shown fake infection warnings and pressured into installing “security” software that was actually malware—a clear example of scareware distributed via legitimate ads.
From 2010 onwards, various industry reports indicated that billions of infected ad impressions were already being reported on thousands of websites, with a significant jump in 2011 when platforms like Spotify suffered no-click auto-download attacks.
In the following years, major news portals and online services fell victim to malvertising campaigns: the Los Angeles Times, Yahoo.com (with the CryptoWall ransomware involved), networks like Google DoubleClick and Zedo, dating sites, adult video portals, MSN, and even the BBC's English-language website. Some studies estimated that, around 2015, more than a third of the world's most visited websites had served some type of malicious advertisement.
One particularly notorious case was that of Zirconium, a threat actor that, according to various sources, purchased around one billion ad impressions in 2017 , using forced redirects to send users to scam or malware websites. It is believed that this single campaign was present every week on more than half of all ad-monetized websites.
More recently, criminals have become even more creative: repurposing abandoned domains to serve malicious ads, embedding cryptomining scripts in banners, relying on services like Coinhive to mine cryptocurrencies in the background, and generally adapting to an ecosystem where programmatic advertising makes control increasingly complex.
How malvertising can affect you
The really important question is: what can happen if your device is affected by malvertising? The short answer is that the consequences can be very serious , both personally and for your business. The malicious payload that reaches your device depends on the attacker's objective and your profile as a victim.
Among the most common threats distributed by malicious advertising campaigns are malware in all its variants : banking trojans to steal credentials and payment data, ransomware that encrypts your files and demands a ransom in cryptocurrencies, spyware that monitors your activity, keyloggers that record everything you type, etc.
It's also common to find malware that floods your browser with banners and pop-ups, redirects your searches to sponsored pages, or manipulates results to trick you into clicking where you don't want to. In addition, there are "classic" viruses and worms that spread between devices, although nowadays the focus is more on threats with a direct financial return.
Another growing trend is malicious cryptocurrency mining (cryptojacking): malware installs itself silently and uses your computer's resources to mine cryptocurrency , sending the profits to criminals. This degrades the performance of your computer or mobile device, increases energy consumption, and reduces the lifespan of your hardware.
In the corporate world, malvertising can be the gateway to compromising internal networks, stealing sensitive data, corrupting critical information, or even paralyzing an organization's operations. That's why, increasingly, companies of all sizes are becoming priority targets for these campaigns, not just home users.
Vulnerable platforms and devices
For years, Windows has been the primary target of malware attacks in general, and malvertising in particular, simply because it has a massive user base . However, thinking that other systems are safe is a mistake that can be costly.
Malicious advertising campaigns targeting specific browsers or add-ons can affect Macs, Chromebooks , Android phones , iPhones , and tablets . In the case of macOS, for example, there have been many campaigns involving fake Flash updaters and scareware specifically designed for that environment.
Mobile devices are especially attractive to attackers because they are always connected, accompany users everywhere, and are commonly used for shopping, online banking, and sensitive communications . Furthermore, many people don't have the same level of security on their mobile devices as they do on their computers, nor do they update their operating systems or apps as frequently.
In business environments, where all types of equipment (PCs, laptops , corporate mobiles, tablets, etc.) coexist and personal and financial data is handled, the impact of a malvertising attack can be enormous. Some reports have indicated increases of more than 50% in these types of incidents targeting companies during certain periods, showing a clear trend of attackers targeting corporate objectives.
Common methods of malicious code injection
To inject their code into the advertising chain, attackers have a wide range of entry points. They don't limit themselves to just visual creative; they exploit any link in the ad supply chain where they can introduce scripts or redirects.
A common approach is to compromise ad requests: every time a user visits a page, the site requests ads from different third-party providers. If one of those providers has been compromised, it can inject malicious code into the response , contaminating the ad that will be shown to the user.
Another avenue is through the creative elements themselves: banners that combine images and JavaScript can contain embedded scripts that execute downloads or redirects upon loading. It's also common for ad landing pages to contain exploits or malware kits designed to attack as soon as the user arrives.
Behind the scenes, many ads pass through several URLs before displaying the final page: tracking systems, redirectors, affiliate platforms, etc. If any of these intermediate steps are compromised, it can inject its own malicious code into the chain , leading to unauthorized downloads or data exfiltration.
Even tiny elements like tracking pixels (small snippets of code used to count impressions or collect statistics) can be abused. If an attacker hijacks these pixels, they can intercept or modify the data flow , or use them as a gateway for hidden redirects.
How to detect and stop malvertising
Although some malicious advertising attacks are very sophisticated, there are a number of measures that can help you drastically reduce the risk of infection, whether you are an end user or manage an ad-supported website.
On the user side, the first line of defense is to have a good antivirus or security suite that analyzes web traffic in real time, blocks known malicious sites, and detects suspicious downloads before they run. Many modern solutions use cloud-based analytics and reputation systems to quickly identify new malvertising campaigns.
Another very effective tool is ad blockers and anti-tracking extensions . By preventing banners, pop-ups, and advertising scripts from loading, you minimize the attack surface. As a side effect, you'll improve loading speed, save mobile data, and limit the tracking of your online activity.
Configuring your browser so that plugins (such as Flash or Java, if still in use) only run on demand via the "click-to-play" function adds an extra layer of protection: active content is not loaded automatically, so many exploitation attempts are thwarted.
Finally, it is essential to keep your operating system, browser, plugins, and applications always up to date . Most download campaigns rely on known vulnerabilities for which patches already exist, but which remain exploitable because many users do not update their systems frequently enough.
Good practices for preventing infections
Besides technical measures, your browsing habits and attitude towards the internet make all the difference. A little skepticism and good digital habits will save you from many unpleasant surprises related to malvertising.
First, be wary of ads that ask for immediate downloads, request personal data without a clear reason, or offer products and services with absurd discounts or for free . Nobody gives anything away for free: if a banner seems too good to be true, it's very likely a trap.
Get into the habit of downloading programs, updates, and apps only from official websites or recognized stores (App Store, Google Play, manufacturer websites, etc.). Avoid third-party download sites and, of course, never install anything that arrives via a pop-up ad, no matter how convincing it may seem.
Disable or uninstall plugins you don't use, especially those that have historically been a magnet for exploits (Flash, Java, old media players, etc.). The less unnecessary software you have, the smaller the attack surface you offer to cybercriminals.
Finally, strengthen security with strong passwords for your antivirus and other critical programs, and promote cybersecurity training and awareness both personally and within your company. Knowing the warning signs of malvertising and common social engineering techniques is a very effective barrier.
Malicious advertising takes advantage of the complexity of the advertising ecosystem and the trust we place in legitimate websites, but with an updated system, good security software, well-configured ad blockers, and a cautious attitude towards suspicious offers, it is possible to browse with much more peace of mind and minimize the impact of one of the most silent and widespread threats on the internet.

Table of Contents
- 1 What is malvertising or malicious advertising?
- 2 How a malvertising attack works
- 3 Types of campaigns and malvertising techniques
- 4 Malvertising versus adware: what are the differences?
- 5 History and evolution of malvertising
- 6 How malvertising can affect you
- 7 Vulnerable platforms and devices
- 8 Common methods of malicious code injection
- 9 How to detect and stop malvertising
- 10 Good practices for preventing infections
