- WPR is responsible for recording very detailed ETL traces of the behavior of Windows using predefined or custom profiles.
- WPA allows for in-depth and visual analysis of ETL traces using graphs, pivot tables, filters, and view profiles.
- The combined use of WPR and WPA is key to detecting CPU spikes, memory problems, leaks, and bottlenecks. Boot or energy.
- WPA views, charts, and tables can be customized to focus on specific scenarios such as slow boot, GPO, modern standby, or heavy CPU usage.

Thoroughly monitoring Windows performance is no longer just for developers ; with the Windows Performance Recorder (WPR) and Windows Performance Analyzer (WPA) tools, you can capture and dissect exactly what's happening on your computer when the CPU spikes, boot times are incredibly slow, or annoying micro-freezes occur.
While the classic Performance Monitor or perfmon falls somewhat short for certain scenarios, WPR and WPA form a tandem designed for demanding profiles : administrators, systems engineers, or advanced users who want accurate data, highly detailed ETL traces, and a powerful analysis interface to get to the root of the problem without shooting in the dark.
What are WPR and WPA and what exactly are they used for?

- Windows Performance Toolkit (WPT) is the Microsoft package that combines WPR and WPA, two independent utilities but designed to work together and generate very fine profiles of the behavior of the operating system and applications.
- Windows Performance Recorder (WPR) is the component responsible for recording the traceIt relies on Event Tracing for Windows (ETW) to record events from CPU, memory, disk, network, power and other subsystems, generating ETL files that are then calmly analyzed.
- Windows Performance Analyzer (WPA) is the advanced viewer and analyzer of those ETL tracesIt offers an interface with interactive graphics, pivot tables, filters, full-text searches, and an Issues window that helps locate root causes in certain scenarios.
- Although Xperf (line of commands (inherited) still exists, its Xperfview viewer is no longer supportedNowadays, all visual analysis is done with WPA, which is much more flexible, modern, and powerful.
- In terms of requirements, the environment is quite reasonable.WPR and WPA are designed for Windows 8 or later, and WPA also requires .NET Framework 4.5 or later. The command-line version of WPR (WPR.exe) is included with Windows 8.1 and later, while the graphical interface for WPR and WPA is obtained by installing the Windows Assessment and Deployment Kit (WADK).
Installing and accessing WPR and WPA on Windows
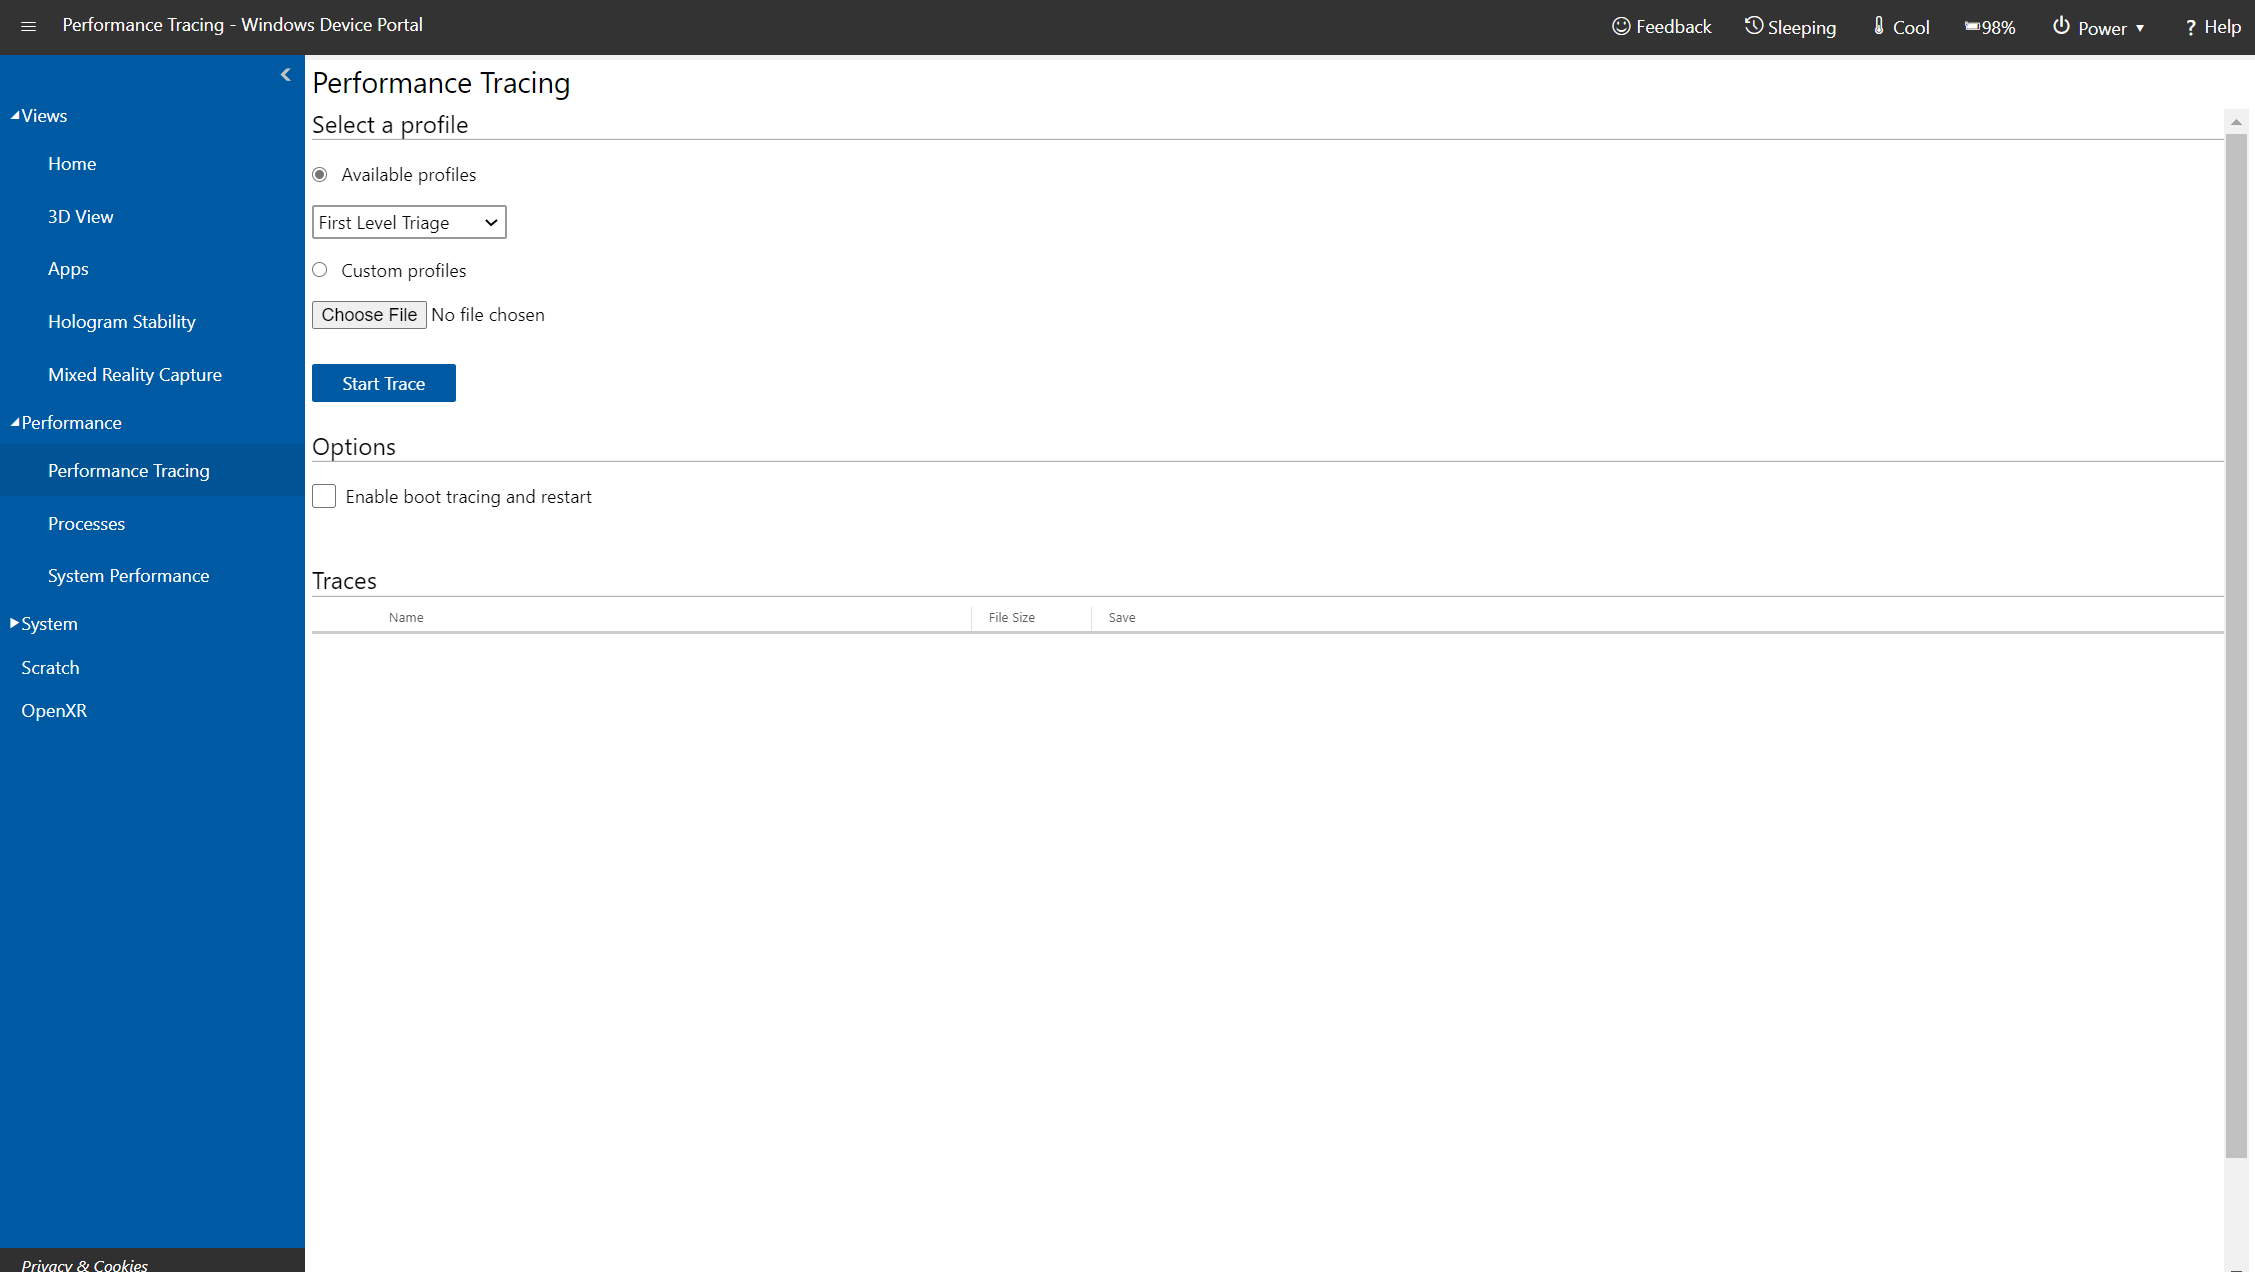
To fully utilize the graphical capabilities of these tools, it's advisable to install the Windows Performance Toolkit from the ADK . During the Windows ADK installation, simply select the Windows Performance Toolkit component to obtain WPR (UI) and WPA.
Once installed, accessing WPR in Windows 10 or Windows 11 is very simple : you can type "Windows Performance Recorder" in the Start menu and launch the graphical application (WPRUI.exe), or use WPR.exe from a command prompt if you prefer scripts and automation.
In WPR's graphical interface, you'll see a simple panel with scenarios or profiles to choose from , such as CPU usage, power issues, overall system performance, or memory usage. Clicking "More options" displays advanced parameters to adjust what will be logged, at what level of detail, and for how long.
At the bottom, you can add or remove additional recording profiles if you need to mix several sets of events (for example, CPU + memory + disk). Once you know what you want to capture, start recording by clicking the "Start" button.
WPA, on the other hand, can be found by searching for "Windows Performance Analyzer" in the Start menu . You can also open WPA directly after completing a WPR recording, using the "Open in WPA" option that appears when you save the ETL file.
How to record performance data with WPR
The typical workflow always starts with a recording using WPR , either from the graphical interface or from the command line, depending on how formal or automated you want to make the process.
With the graphical interface (WPRUI.exe), the standard procedure is very straightforward : you choose a predefined profile such as "First level triage" (basic priority assessment) or one specific to CPU, memory, power, modern standby, etc., and click Start to begin the capture.
If you need more control, the "More options" button lets you configure details : duration, level of detail (light, detailed), inclusion of call stack (stack walking), circular or continuous logging, and even custom profiles defined in XML for very specific scenarios.
During recording, WPR will show you the elapsed time , buffer size, and number of recorded events , which is very useful for ensuring that you don't get carried away with excessively long tracking that could generate giant files.
To stop and save the session, click "Save ." At this point, WPR will ask you where to store the ETL file and usually displays a box to add a description of the problem (for example, "CPU spike when opening Excel" or "Very slow domain login"). You can then choose between opening it directly in WPA or closing it and analyzing it later.
Capture traces from the command line using WPR.exe
If you work in enterprise environments or want integration with scripts and automations , the WPR.exe console version is key, as it allows you to start and stop traces from scripts, GPOs, scheduled tasks, or orchestration tools ( modifying services in Windows 11 ).
The basic usage pattern is very simple : you run "wpr -start Profile" to start a trace, reproduce the problem you want to study, and then run "wpr -stop name.etl" to save the file.
A common example is the analysis of power or modern standby problems . In that case, WPT is installed, an elevated command prompt is opened, the installation folder is navigated to, and a command such as the following is executed:
`wpr -start Power` to start logging data related to power, CPU states, devices, and standby activity; in these analyses, it may be useful to review power settings such as enabling high performance mode.
After leaving the system in modern standby mode for at least an hour , the computer is woken up and wpr -stop TrackingPower.etl is launched to shut down and store the trace, which will then be examined in WPA.
Open and explore ETL files in Windows Performance Analyzer
With the ETL file in hand, the next logical step is to open it in WPA to begin the visual analysis. You can do this in two ways: directly from the WPR save wizard (using the "Open in WPA" option) or by launching WPA and using the File > Open menu, or the keyboard shortcut Ctrl + O.
The WPA interface is organized around a central work area with Analysis tabs , surrounded by several dockable windows that can be shown or hidden from the Window menu, such as the Graph Explorer, Analysis Wizard, Problems, Details, or Diagnostic Console.
The Graph Explorer contains thumbnails of all available graphs for that trace , grouped by categories (CPU, memory, I/O, power, devices, etc.). Clicking the small triangle next to a category expands the related graphs.
To analyze a chart in detail, simply drag it from the Chart Explorer to the Analysis tab or double-click it. The chart will then appear in full size on the tab, along with an associated data table that behaves like an advanced pivot table.
In each chart, you can choose the layout using the icons in the upper right corner : chart only, table only, or both. This is very useful when you need to see the visual trend and, at the same time, filter very specific data in the table.
Time management: selection, zoom, and highlighting in WPA
One of the key features of WPA is that all graphs on the same Analysis tab share the same time scale , making it easier to correlate events between different subsystems (CPU, disk, network, power, etc.).
To select a specific interval of the trace, drag the mouse horizontally over an area of the graph . This selection will be reflected on the timeline at the bottom of the tab.
If you want to zoom in on that section to see it in more detail, right-click on the selection and choose "Zoom to selected time range" . You can repeat this operation several times, zooming in to very small intervals that allow you to see even micro-peaks of activity.
When you need to visually highlight a range across all charts at once , you can use the highlight selection option: right-click on the range and select "Highlight selection." This selection will remain even if you later click on other points in the chart or change the view.
To clear that marker, right-click on the interval again and select "Clear Selection ." This is a very convenient way to focus attention on a boot phase, a CPU spike, or a modern waiting period without losing reference when moving your view.
Advanced customization of data tables
WPA tables are true pivot tables with far more power than they initially appear . Each column can be dragged, sorted, converted into a key or data field, and its structure is also reflected in the legend of the associated chart.
You can sort by any column by clicking its header ; clicking again reverses the order (ascending/descending). This is very useful for answering questions like "which process is using the most CPU?" or "which device has been active the longest during modern wait?"
Right-clicking on the table header opens the "Column Selector" , where you choose which columns are displayed and can save or apply predefined sets of columns so you don't have to set up the table from scratch every time.
Inside the table, you'll find two vertical colored bars (gold and blue) . The columns to the left of the gold bar are considered key (dimensions by which the information is grouped), while the columns between the gold and blue bars contain the actual numerical data. The elements displayed in the chart are typically located to the right of the blue bar.
Dragging a column to the left of the gold bar makes it a key , so the table regroups and the chart adjusts its legend accordingly. Similarly, some columns can be dragged to the chart elements area to be visually represented.
Views, profiles, and window management in WPA
If you want to compare the same trace with different timescales or graph combinations , you can open multiple Analysis tabs. From the Window menu, select "New Analysis View" and drag the graphs you want to isolate to that new tab.
From the Window menu, you can also open or close various auxiliary windows (Graphs Explorer, Analysis Wizard, Problems, Details, Diagnostic Console). If you've closed something by mistake, simply re-select it from that menu.
Once you have built a layout of graphs, tables, and windows that is comfortable for a type of analysis (e.g., CPU performance or energy analysis), it is highly recommended to convert it into a "view profile".
In the Profiles menu, you'll find options like Export, Apply, and Save Startup Profile . Export creates a file with the current layout of charts and columns; Apply loads a previously saved profile; Save Startup Profile automatically applies that view every time you open WPA, ideal if you frequently perform the same type of diagnostic.
The Diagnostic Console is another useful window, as it collects exceptions and problems during the analysis , especially those related to symbol loading and decoding . If something goes wrong when interpreting call stacks, this console usually provides clear clues as to what is happening.
Searching, filtering, and working with legends
When the plot is large, intelligent filtering is vital to avoid getting lost among thousands of rows . WPA offers several filtering and search options both from the chart legend and from the data tables themselves.
In the chart legend, you can activate or deactivate specific elements by right-clicking on them. This way, you only see the processes, devices, or triggers you're interested in, reducing visual clutter.
In the table, if you select one or more rows and right-click, you have the option to "Filter to selection ." This creates a view restricted to those items, perfect if, for example, you want to focus only on a suspicious process or a problematic network device.
The text search function is also activated by right-clicking on the table and using "Find," "Find Next," or "Find Previous." This allows you to quickly locate processes by name, group tags, paths, etc.
Additionally, you can fix a subset of columns using gray freeze bars : right-click to display them, and then drag these bars to delimit which columns remain fixed while you scroll horizontally through the rest – very practical in wide tables.
Loading symbols and user preferences
For call stacks to be truly useful, WPA needs to load symbols , both from the system itself and, optionally, from third-party binaries. This allows memory addresses to be translated into human-readable function names.
In the tracing or advanced settings menu, you can enable symbol loading and define symbol paths (for example, Microsoft symbol servers, local folders, etc.). This allows WPA to automatically resolve symbols and display much richer information when you open a trace.
If something goes wrong or takes too long, the Diagnostic Console will display errors or symbol download warnings , so it's a good idea to keep it in view when working with complex stacks or non-standard versions of binaries.
These preferences are saved for future sessions , making it easy to repeat analyses with the same symbol resolution conditions without having to reconfigure each time.
Real-world scenarios: CPU high load, memory leaks, and drivers
Beyond theory, WPR and WPA shine in very specific performance problem scenarios , where other monitors do not reach the level of detail needed to see the root cause.
To investigate high CPU usage , the default first-level profile or the specific "CPU Usage" profile in WPR is typically used. Then, in WPA, the key graph is "CPU Usage (Sampled)" or "CPU Usage (Precise)" depending on the capture type.
In these graphs, it is common to work with keys such as process stack, thread identifier, or process names , and to sort by CPU sample count to find out which threads and functions are monopolizing the processor.
For virtual memory (VirtualAlloc) leaks , the VirtualAlloc usage profile and the "virtualAlloc Commit Lifetimes" graph are used, examining columns such as Type, Process, and Stack, and data such as count and total size affected in MB.
Kernel memory leaks (pools) are addressed using pool usage profiling , which is analyzed with "Pool Usage" graphs. Relevant keys include type (paged/non-paged), pool label, and stack size, and are sorted by count and size to detect which label is growing uncontrollably.
Regarding handle leaks, there's a specific handle usage profile associated with "Handle Usage" graphs. These graphs focus on columns such as the creating process, handle type, and creation stack, examining object name, identifier, and number of handles.
Slow startup, GPO, and login problems
One of the most common headaches in domain environments is endless boot times and very slow logins , often related to complex GPO processing, blocking drivers, network latencies, or applications that get stuck.
In these cases, the recommended strategy usually combines WPR/WPA with other specific tools such as GPLogView, uberAgent-type solutions, SysTrack, Nexthink or digital experience platforms, and, where appropriate, techniques to disable unnecessary services that slow down startup.
A practical workflow would be to launch a trace with WPR just before the problematic boot (or configure it to start on boot), let the system complete the domain login, and stop the trace once it is "stable" on the desktop.
Next, in WPA, CPU, disk, controller, and service graphs are analyzed in the time window corresponding to the boot , looking for which processes or services are consuming CPU time or blocking the main thread for long intervals.
If you suspect GPO, you can correlate policy processing events with network and service activity , although for a breakdown by CSE (Client Side Extension) it is usually useful to supplement with specific group policy logs or specialized tools that directly measure the duration of each extension.
Modern standby mode and DRIPS graphics on WPA
Modern devices with connected standby mode have their own performance and battery consumption challenges ; here WPR with its power profile and WPA with its specific graphics are practically indispensable.
After capturing a long modern standby trace, WPA offers graphs such as "Platform Idle State" and "DRIPS" to understand what is preventing the system from staying in deep low-power states.
The "Platform Idle State" graph shows the platform's residence time in different idle states over time . The most important state is the deepest, known as DRIPS, which represents the lowest level of SoC power consumption.
The higher the percentage of time spent in DRIPS mode, the better the standby time . A percentage above 90% is usually a sign of good performance; below 80% warrants further investigation. To view this, open the graph's table view and filter by state, examining the percentage of battery life column.
The DRIPS graph, on the other hand, lists active components (triggers, devices, processes) that keep the system awake . Triggers are software mechanisms authorized to execute tasks while the system is idle (such as notification services or synchronization agents).
In the table in that chart, the Reason Time Percentage column indicates which trigger or device has been active the longest . For example, you might see that an agent service (BI), WNS, NCSI, or an image download manager is occupying 40% or 50% of the time, blocking entry into DRIPS.
Devices, energy states and correlation with SleepStudy
In addition to software activity, physical devices also play a key role in whether or not a device enters DRIPS . WPA displays device power states (D0-D3) and allows you to identify those that remain in high power consumption.
The "Device Dstate" graph lists the Windows Power Framework (PoFx) devices that have been active during the modern standby session. Examining the Reason Time Percentage column identifies the most problematic ones.
WPA also integrates seamlessly with reports generated by SleepStudy . Many SleepStudy concepts (triggers, processors, device functions, PDC phases, networks, power requests) have a direct mapping to WPA graphs, such as PDC resistor activity, CPU idle states, Device Dstate, or Power Requests.
Thanks to that correlation, you can go from a high-level summary in SleepStudy to a low-level analysis in WPA , seeing exactly which sessions, processes, or devices have turned on the system and for how long.
By combining WPR's powerful capture capabilities with WPA's visual analysis capabilities, it's possible to dissect almost any Windows performance issue with pinpoint accuracy : from seemingly random CPU spikes and elusive memory leaks to slow boot times caused by Group Policy Objects (GPOs) or excessive battery drain in modern standby mode. While the learning curve is somewhat steeper than with other utilities, once you've mastered the workflow—record ETL > open in WPA > select graphs > filter and drill down—it becomes an invaluable tool for demanding home environments and, especially, for enterprise scenarios where data is needed to identify who or what is degrading the user experience.


Passionate writer about the world of bytes and technology in general. I love sharing my knowledge through writing, and that's what I'll do on this blog, show you all the most interesting things about gadgets, software, hardware, tech trends, and more. My goal is to help you navigate the digital world in a simple and entertaining way.
Table of Contents
- 1 What are WPR and WPA and what exactly are they used for?
- 2 Installing and accessing WPR and WPA on Windows
- 3 How to record performance data with WPR
- 4 Capture traces from the command line using WPR.exe
- 5 Open and explore ETL files in Windows Performance Analyzer
- 6 Time management: selection, zoom, and highlighting in WPA
- 7 Advanced customization of data tables
- 8 Views, profiles, and window management in WPA
- 9 Searching, filtering, and working with legends
- 10 Loading symbols and user preferences
- 11 Real-world scenarios: CPU high load, memory leaks, and drivers
- 12 Slow startup, GPO, and login problems
- 13 Modern standby mode and DRIPS graphics on WPA
- 14 Devices, energy states and correlation with SleepStudy